For SaaS & API teams

Know what every deploy changed.

New scripts, heavier bundles, new APIs, new third parties and broken flows, seen from the browser before your customers notice.

Available today

Built for apps, not just websites.

Everything below is in EPIC now. The badge shows the plan that includes it.

Observe

Deploy check

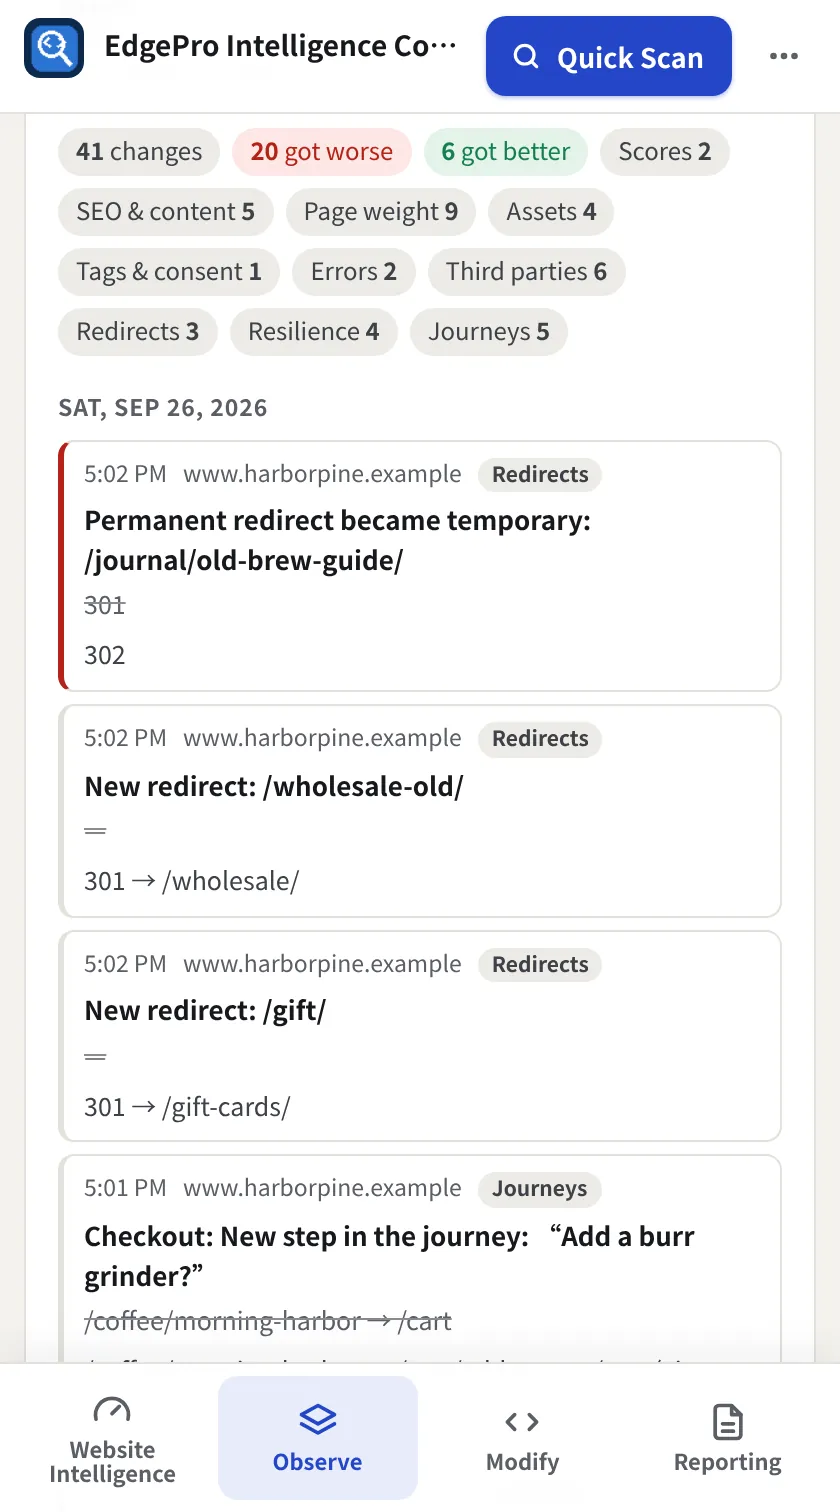
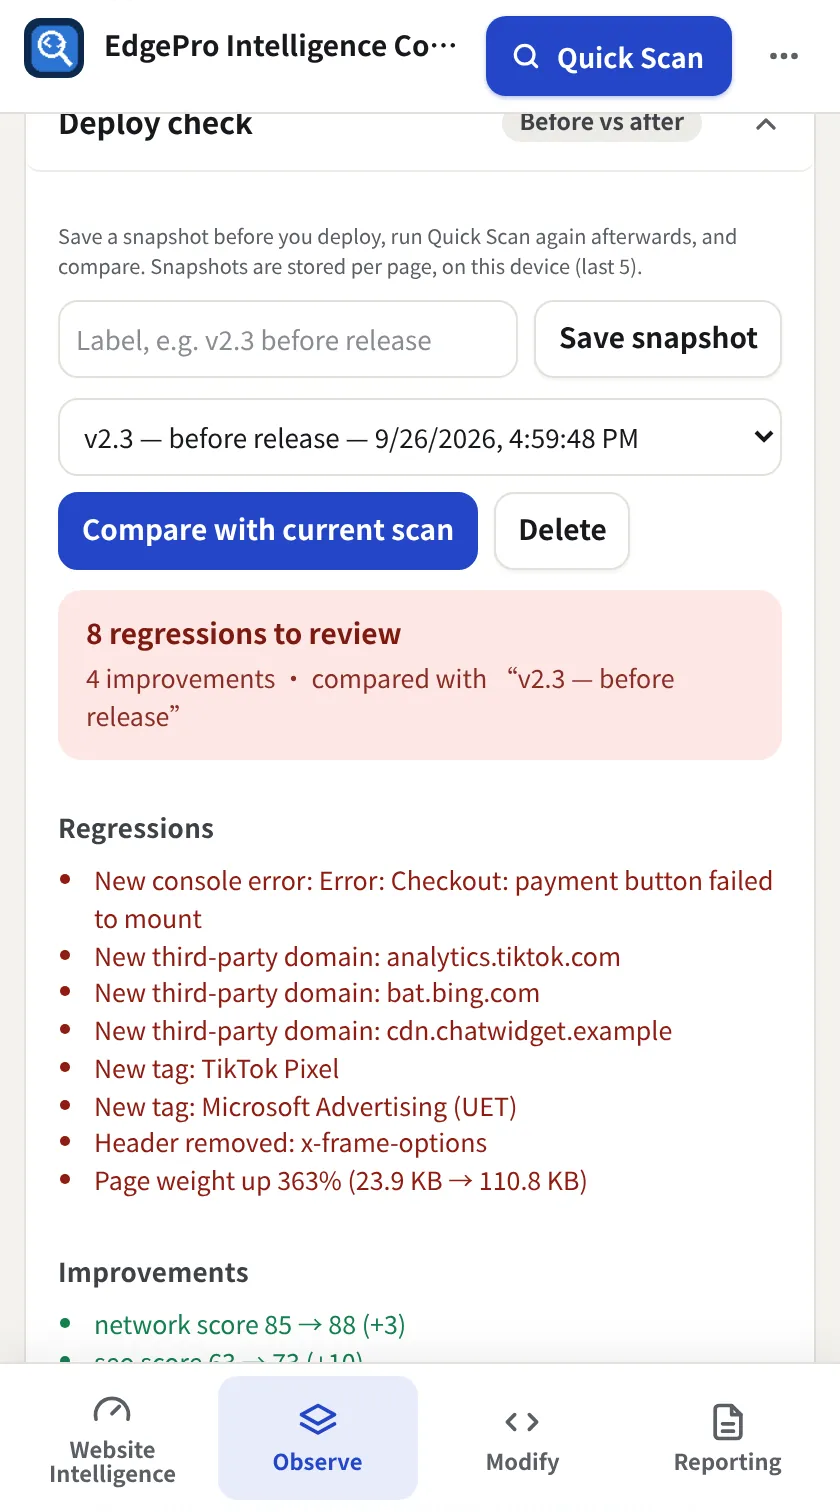
Save a snapshot, ship, rescan. Console errors, failed requests, speed and every new or changed file, as one list of regressions and improvements. Copy it as a GitHub or Jira issue.

Observe

Every file, every size

New, removed and grown files between scans, down to 1 KB. Renamed builds such as app.3f9a.js → app.7d2e.js are matched, so you see “app.js grew 240 KB”, not noise.

Modify

Every API on the screen

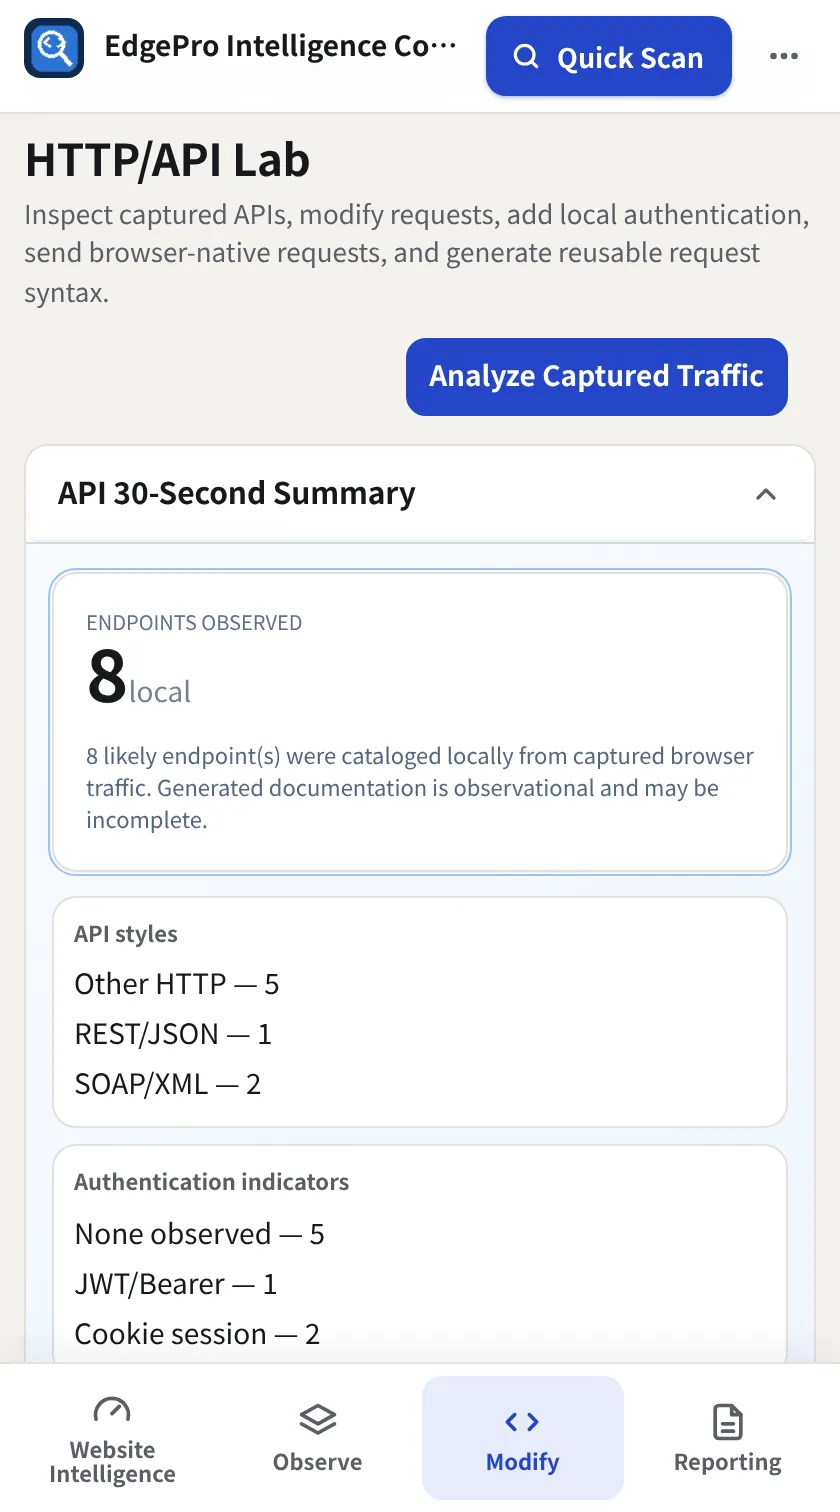
The HTTP/API Lab lists every call a screen makes: REST, GraphQL, SOAP, OData or WebSocket, with status, timing and how it's authenticated. Replay or edit any request and copy it as cURL, fetch or Python.

Observe

API & session security

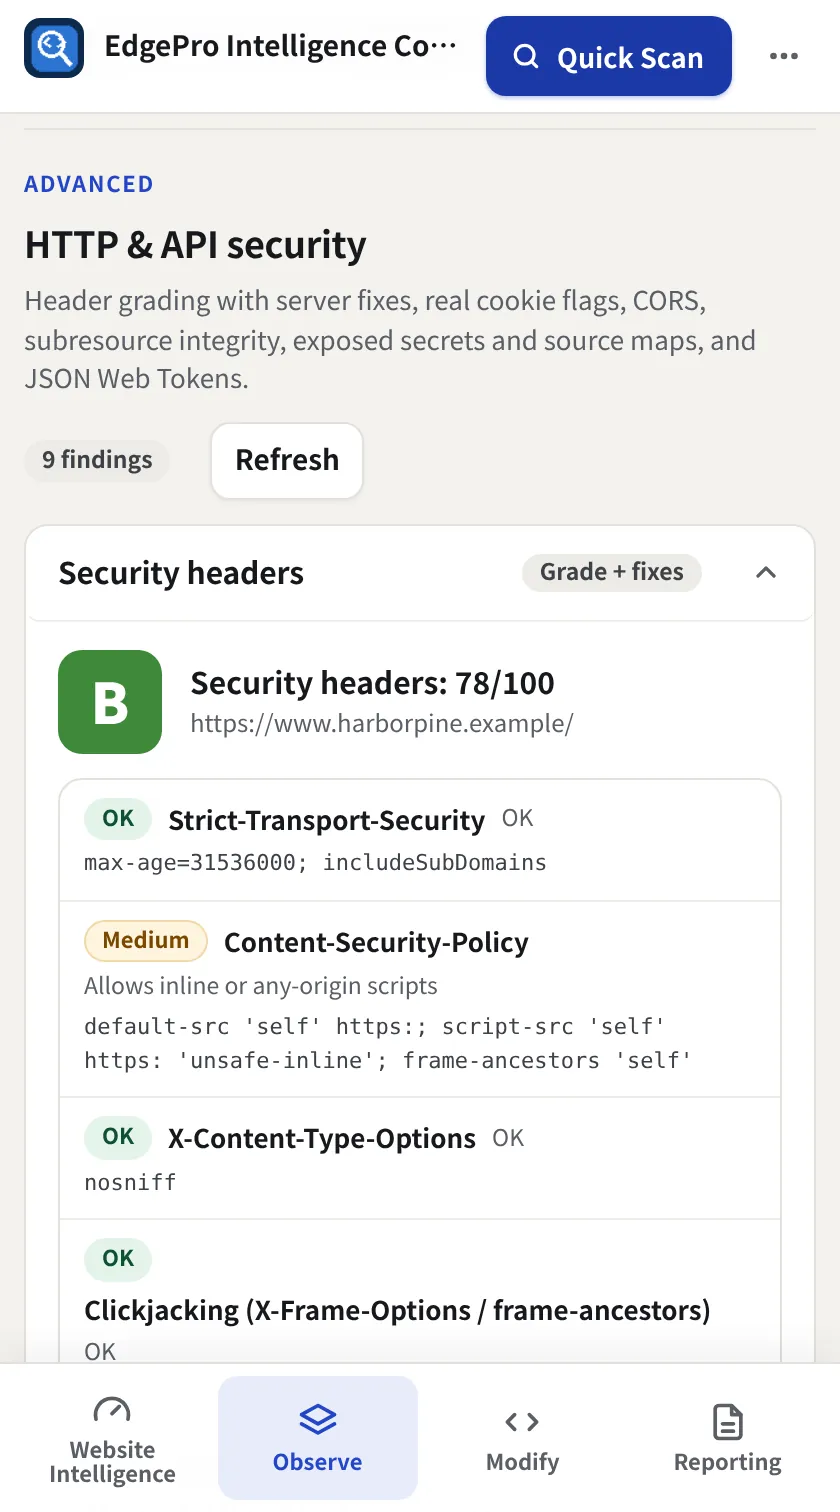
CORS that lets other sites read your API, JWT weaknesses, session cookie flags, keys and tokens exposed in client code, public source maps, security headers with fixes.

Observe

Third parties in your app

Every outside service your app loads, recognised across 110 known services, with what's new since the last scan and what it added to page weight.

Free

Works where you're signed in

Quick Scan reloads the tab you're on with your existing session, so it analyses the real app screen, not the login page. Nothing is sent to us.

Modify

Test fixes and flags

Change request and response headers, cookies (feature flags, sessions), HTML, CSS or JavaScript, or block a script, in your own browser only.

Observe

Sign-up and upgrade flows

Record your sign-up or upgrade flow on your marketing site once; EPIC re-checks it on a schedule and never submits the form.

Observe

Ready for a launch spike

A resilience score from caching, CDN, rate-limit and error-handling evidence. Read-only: EPIC never sends load or attack traffic.
Deploy check

Before and after every release.

Snapshot before you ship. Rescan after. EPIC lists what got worse, what got better, and which files changed.

  • New console errors and failed requests, first-party and third-party
  • Bundles and images that grew, and by how much
  • New third-party services and scripts
  • Copy the result as a GitHub or Jira issue, or a PR comment
Deploy check before vs after
Change Log with every file compared
HTTP/API Lab

See the API behind every screen.

Every call the screen made, how it's authenticated, and how long it took. Edit and resend any request from the browser.

  • REST/JSON, GraphQL, SOAP/XML, OData and WebSocket recognised
  • Auth detected: JWT/bearer, Basic, API key, CSRF token, cookie session or none
  • cURL, fetch and Python snippets, secrets masked by default
  • Saved login profiles and snippets stay encrypted on your device
HTTP/API Lab endpoint catalog
HTTP and API security
Coming next

Planned for EPIC 1.1

Built on the same capture EPIC already does.

  • API Watch: an inventory of every endpoint across scans; alerts when a new one appears, with the screen and script that called it, how it's protected and whether it returns sensitive fields
  • Signed-in App Crawl: check every screen of your app, following in-app links and “Next” pages, using safe page loads only
  • Size budgets: set limits for JavaScript, images and total weight; flag any deploy that breaks one
  • Journeys inside apps: let data-loading requests through while still blocking anything that saves or sends
  • Screen-change performance: how fast moving between screens feels, long freezes and memory growth
  • Compare two roles: the same screen as an admin and a regular user, differences highlighted

Planned, not yet available, and subject to change. Buy EPIC for what it does today. See the full list on What's coming.

Scan your app free in 10 seconds.

No account. Your scans stay on your device.